A contract arrives in Legal for review, sits in an inbox for six days, then moves to Finance without the current pricing schedule attached. By the time it is signed, nobody can say who accepted the liability cap, whether Security reviewed the data terms, or which business owner agreed to the renewal notice period. The signatures may be complete, but the decision record is not.
A contract approval workflow gives those decisions a defined owner, a sequence, a deadline and an evidence trail. Its purpose is not simply to move a document from “draft” to “signed.” It is to connect the agreement to the supplier, the commercial commitment, the relevant risk reviews and the people who will live with the result. For a procurement team, that connection is what makes an approval useful six months later, when the question is no longer “Can we sign?” but “Why did we accept this, and what should happen next?”
Start with a complete request, not a forwarded attachment
Most approval delays begin before an approver sees the contract. The request is missing the supplier’s legal name, the full commitment, the business owner or the reason for the purchase. Reviewers then spend their time reconstructing the request instead of deciding it. Structured intake should capture the supplier, agreement type, owner, value and currency, term, renewal mechanism and relevant data-handling questions. The current agreement and supporting schedules should travel with that information, rather than arriving in a separate email.
The intake should also establish what each person is being asked to approve. A business owner can confirm that the scope solves the operational need without accepting a non-standard liability position on behalf of Legal. Finance can review the commitment and funding without deciding whether the supplier’s security evidence is sufficient. Those are connected decisions, not interchangeable signatures. Making the distinction explicit prevents a broad “approved” from concealing an unanswered specialist question.
Route for risk and authority, not value alone
A routine software renewal under an existing agreement should not necessarily follow the same route as a new supplier processing customer data. The latter may need Security and Privacy input before the final commercial approval; the former may need a focused check of scope, pricing and renewal terms. The objective is to involve the people whose decisions matter, with clear routing rules that the team can explain and maintain.
Value is an important input, but it is not a complete measure of exposure. A modest subscription can introduce personal-data processing or a critical system dependency. A larger renewal may sit within a previously reviewed framework. When designing the route, consider the facts that materially change the decision:
- The total commercial commitment, not only the first invoice or annual headline price.
- Whether the supplier is new, and whether existing due diligence covers the proposed service.
- Personal or confidential data, system access and operational criticality.
- Non-standard liability, indemnity or other positions identified during review.
- The term, automatic renewal and the deadline for giving notice.
- Relevant geography, residency requirements and the contracting entity.
These inputs need to be captured and reviewed; they should not depend on an assumption that software will infer every legal or commercial risk from an attachment. Start with a manageable set of questions and conditions. A route that nobody understands is difficult to govern, even if it has a branch for every imaginable scenario.
Make approval authority visible
A delegation-of-authority policy should translate into a clear answer to “Who can approve this commitment?” Thresholds, business units and roles need to reflect the organisation’s policy, rather than whoever happens to be available in an email chain. Before releasing a request, procurement should be able to check the proposed approvers and signers against that policy. Approval authority and signing authority are related, but they are not the same responsibility.
Absence and reassignment need a process too. Define who may nominate a substitute, which limits still apply and what reason must be recorded. The control is not that one named individual must personally handle every request forever. It is that a change of person does not silently become a change of authority. A sensible escalation should resolve a blocked decision while preserving the evidence of who ultimately made it.
Give reviewers the context needed to decide
Finance needs the total commitment, payment schedule, accountable budget owner and the request’s business justification. Legal needs the current document, the positions under discussion and any proposed exceptions. Security and Privacy need a service description, the data involved and the relevant assessment evidence. The business owner needs enough detail to confirm scope, service expectations, implementation responsibilities and exit arrangements. Sending everyone the same bare PDF does not give them the same ability to make a useful decision.
The supplier record should help reviewers find due diligence, contacts, prior agreements and relevant reviews. The contract record should hold the agreement, commercial details, stakeholders and key dates. Access still matters: connected information should be available to the people entitled to see it, not made universally visible in the name of collaboration. Where document intelligence helps answer a question about a contract, a source citation lets the reviewer inspect the supporting passage. It assists the review; it does not accept the risk or grant approval.
Treat exceptions as decisions that need a record
Urgent purchases, supplier paper and unusual commercial terms are ordinary realities of procurement. A useful workflow makes them explicit. What is the exception? Why is it necessary? Who is authorised to accept the residual risk? Is the acceptance limited to this agreement, or does someone intend to reuse it as a precedent? An unexplained comment saying “OK to proceed” answers very little when the circumstances are examined later.
An exception can also create work after signing. A time-limited security acceptance needs an owner and a review date. A commercial concession may depend on a later milestone. A liability position may need to be revisited at renewal. Keep the decision and its follow-up connected to the supplier or contract, so the next owner does not have to rediscover them. Where an assessment produces a risk outcome, that outcome should remain visible on the relevant record alongside its evidence, rather than disappearing inside a completed questionnaire.
Improve cycle time without weakening the decision
Speed matters, but a shorter approval cycle is not automatically a better process. Removing a necessary reviewer can make a dashboard look healthier while leaving the organisation with more exposure. When reviewing performance, distinguish time spent waiting for missing information from time spent making a genuinely complex decision. Sample returned requests, identify repeated gaps and check whether ownership or authority was unclear. Those findings often point to a better intake question or a clearer route, rather than another reminder.
Choose measures your team can substantiate: elapsed time, time waiting at each stage, the reasons for returns and the frequency of exceptions. Treat these as management questions to investigate, not just targets to optimise. Then look beyond signing. Are renewal details complete? Is an owner assigned? Are relevant assessments current? An approval process that finishes quickly but leaves the agreement unmanaged has only completed part of the job.
See what is complete—and what still needs to happen
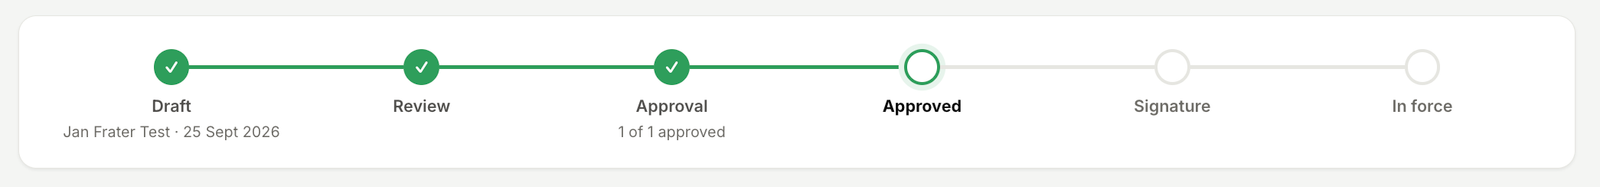
A contract can be approved without being signed, and signed without yet being in force. Treating those states as interchangeable creates avoidable confusion: the business may assume it can start work while procurement is still arranging execution. A visible lifecycle gives everyone a common point of reference. It should distinguish completed stages, the current position and the steps still ahead, so a status update does not require somebody to reconstruct the history from messages.
In the Fratera example below, Draft, Review and Approval are complete, and the current stage is Approved. The approval count confirms that one of one approvals has been obtained. Signature and In force remain ahead. That is a more useful answer than a general “done”: the internal approval decision is complete, but the agreement has not reached the end of its lifecycle. The progress strip provides the overview; the contract’s approvers, signers, documents and dates provide the context for the next action.
Carry the decision into the life of the contract
Signing should move the agreement into active management with its context intact. Confirm the effective date, term, renewal arrangement, notice period, commitment and accountable owners. Where the relationship owner and contract owner are different people, make that distinction visible. An approaching notice deadline should lead to an informed renewal, renegotiation or exit decision—not a scramble to locate the original approval email.
Amendments need the same discipline. If scope, pricing or term changes, identify what is changing, apply the appropriate review and approval, and link the amendment to its governing agreement. Do not assume that an approval of the original contract automatically covers every later commitment. The point of a connected record is to make the history understandable, including the decisions that changed it.
How this fits Fratera
Fratera brings contract records, supplier context, approval routing, delegation of authority, e-signing and renewal actions into one procurement workspace. Standard approvals, signing and intake checklists are included in Core. Pro SRM adds configurable workflows and contract or vendor assessments for teams that need their own questions, conditional review steps and recorded outcomes.
That gives teams a practical foundation for the process described here: collect the request, review the proposed route, put decisions with the right people and retain the context on the relationship being managed. The organisation still defines its authority policy and makes its legal, financial and risk decisions. Fratera connects the work so those decisions do not become isolated events.
A reliable contract approval workflow does more than obtain permission to sign. It leaves the next owner with an intelligible record of what was agreed, which evidence informed the decision and what must happen next. That is the difference between a completed approval and a commitment the business can manage.
See the approval context come together
Follow the contract details, review the people involved and keep the next decision connected to the agreement.
Read the video walkthrough
Find the agreement and enter useful contract context. Review the commercial commitment, approvers and signers. Check the supporting checklist, document and delegation-of-authority information. See what is complete and what comes next: the example is Approved, with Signature and In force still ahead. Keep the contract’s dates, owner and renewal decision connected to the supplier relationship.
Contract approvals in Fratera